For Government
Protect every employee, agency, and citizen.

Urgent: Briefing sign-off needed before 9am
InboxFromMichael Torres <michael.torres@dot-gov-secure.net>
Hi Sarah,
The Secretary’s office needs your sign-off on tomorrow’s briefing document before 9am. It’s under NDA so I can’t attach it – text me at +1 202 456 8819 and I’ll send the secure link.
Michael Torres
Chief of Staff, Dept. of Transportation


Everyone with system access is a target. Protect them.
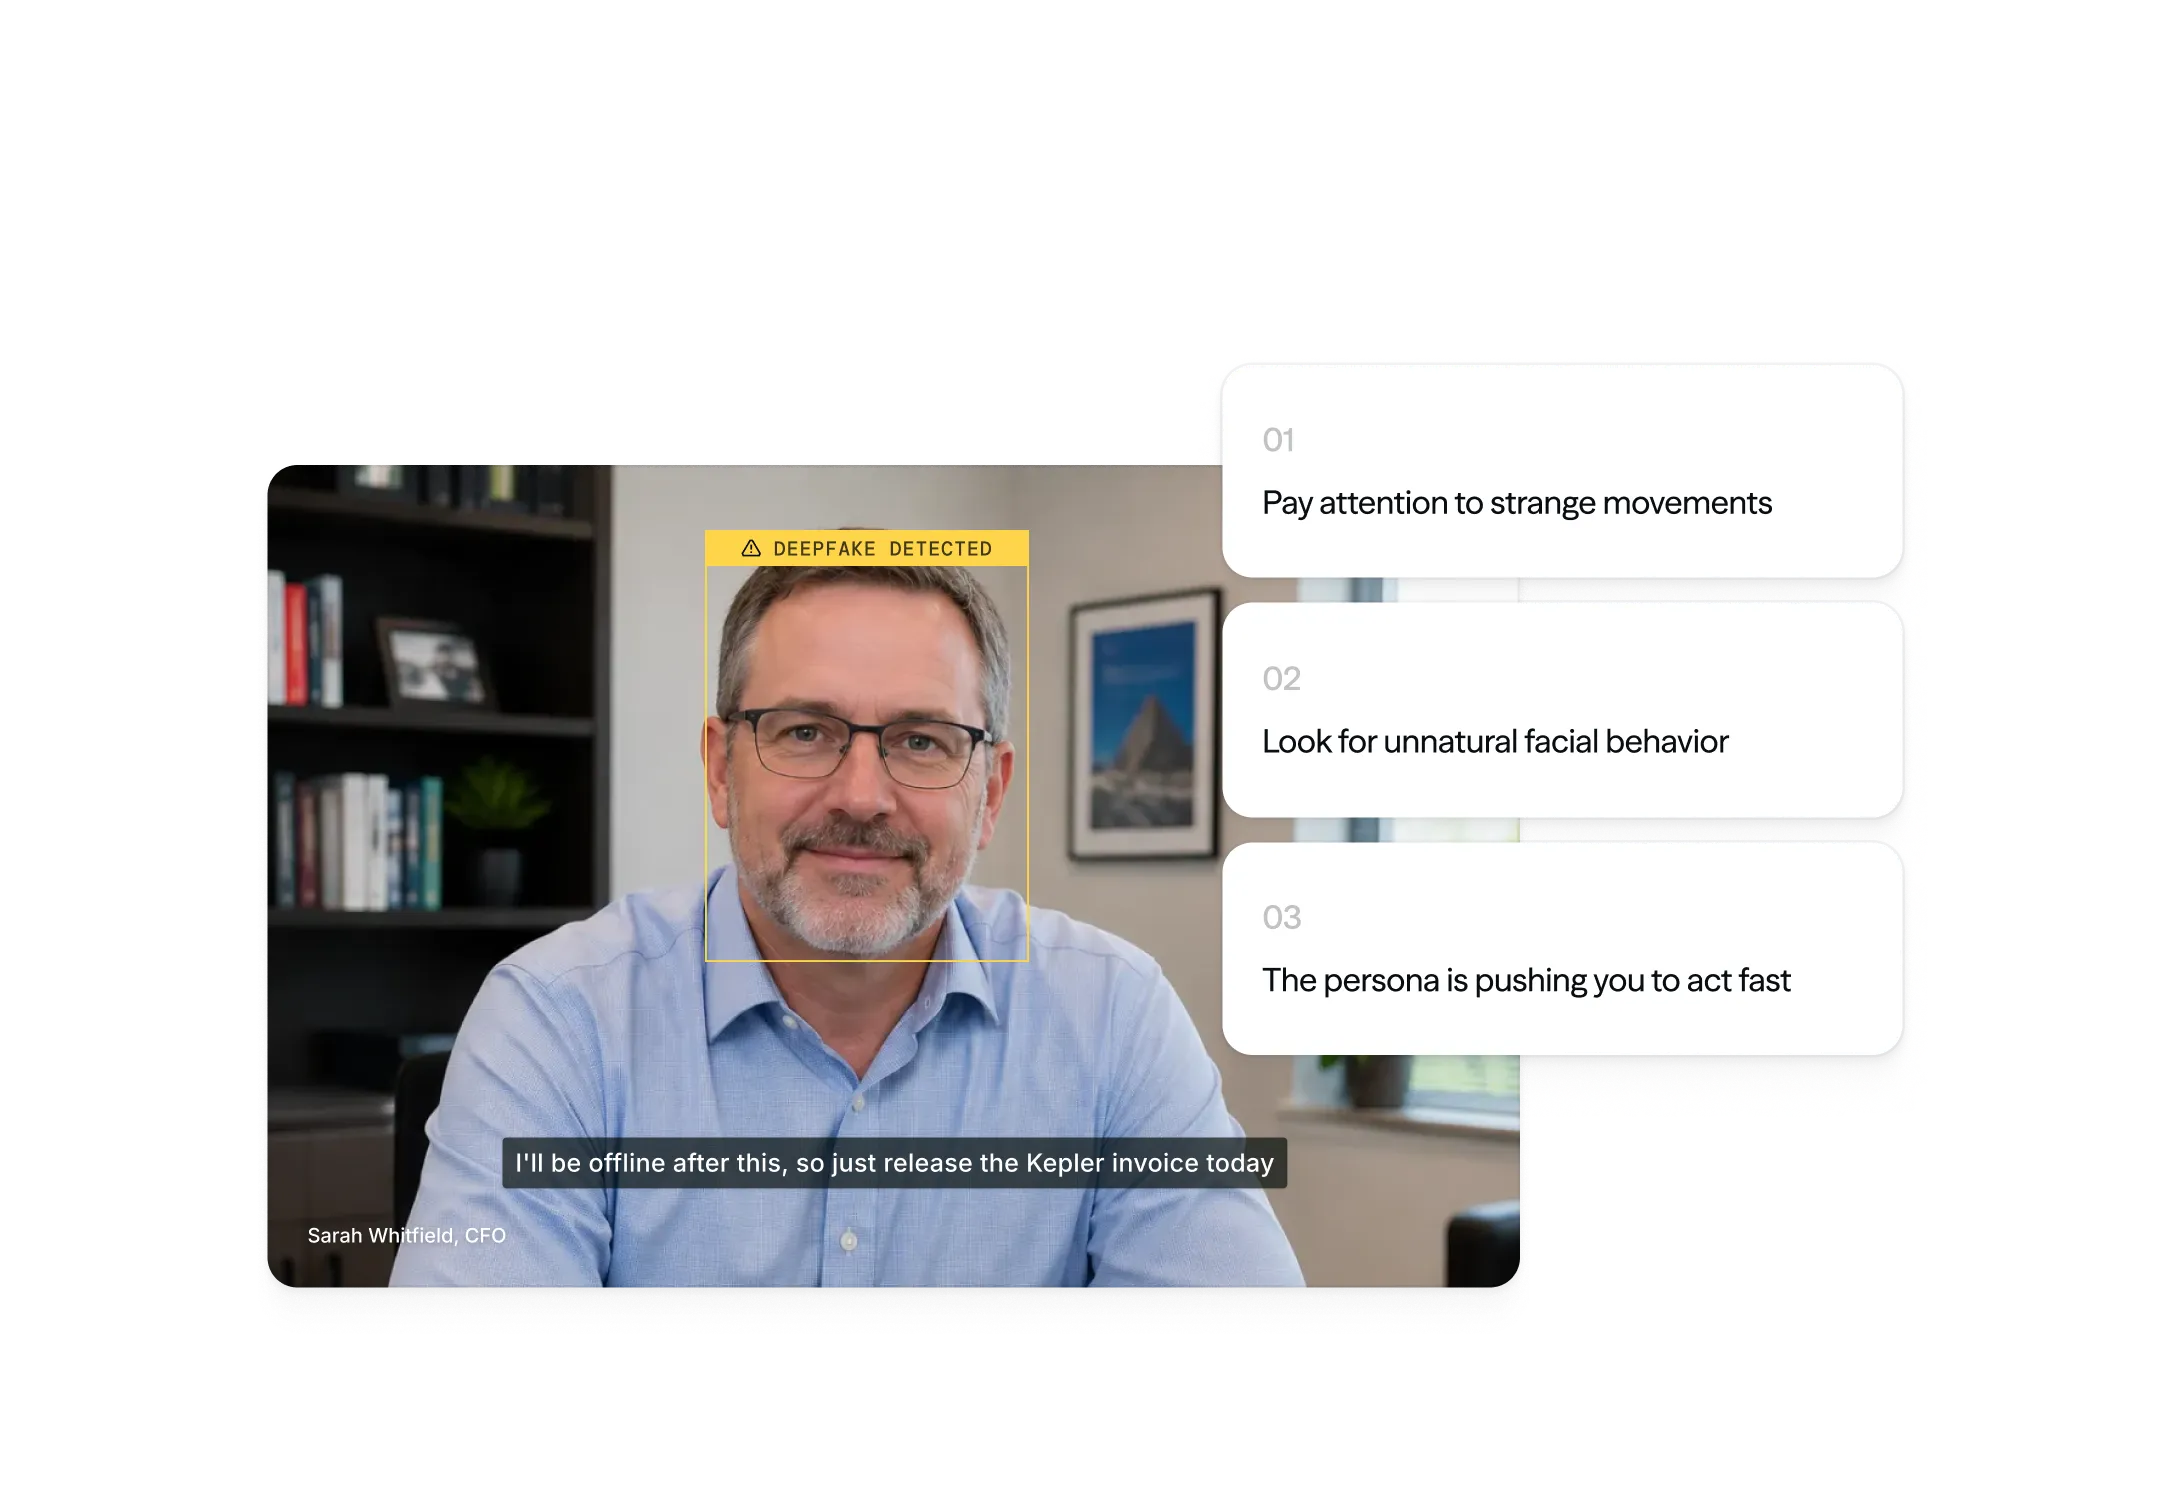
Security Awareness Training
Prepare your team against AI social engineering with interactive training
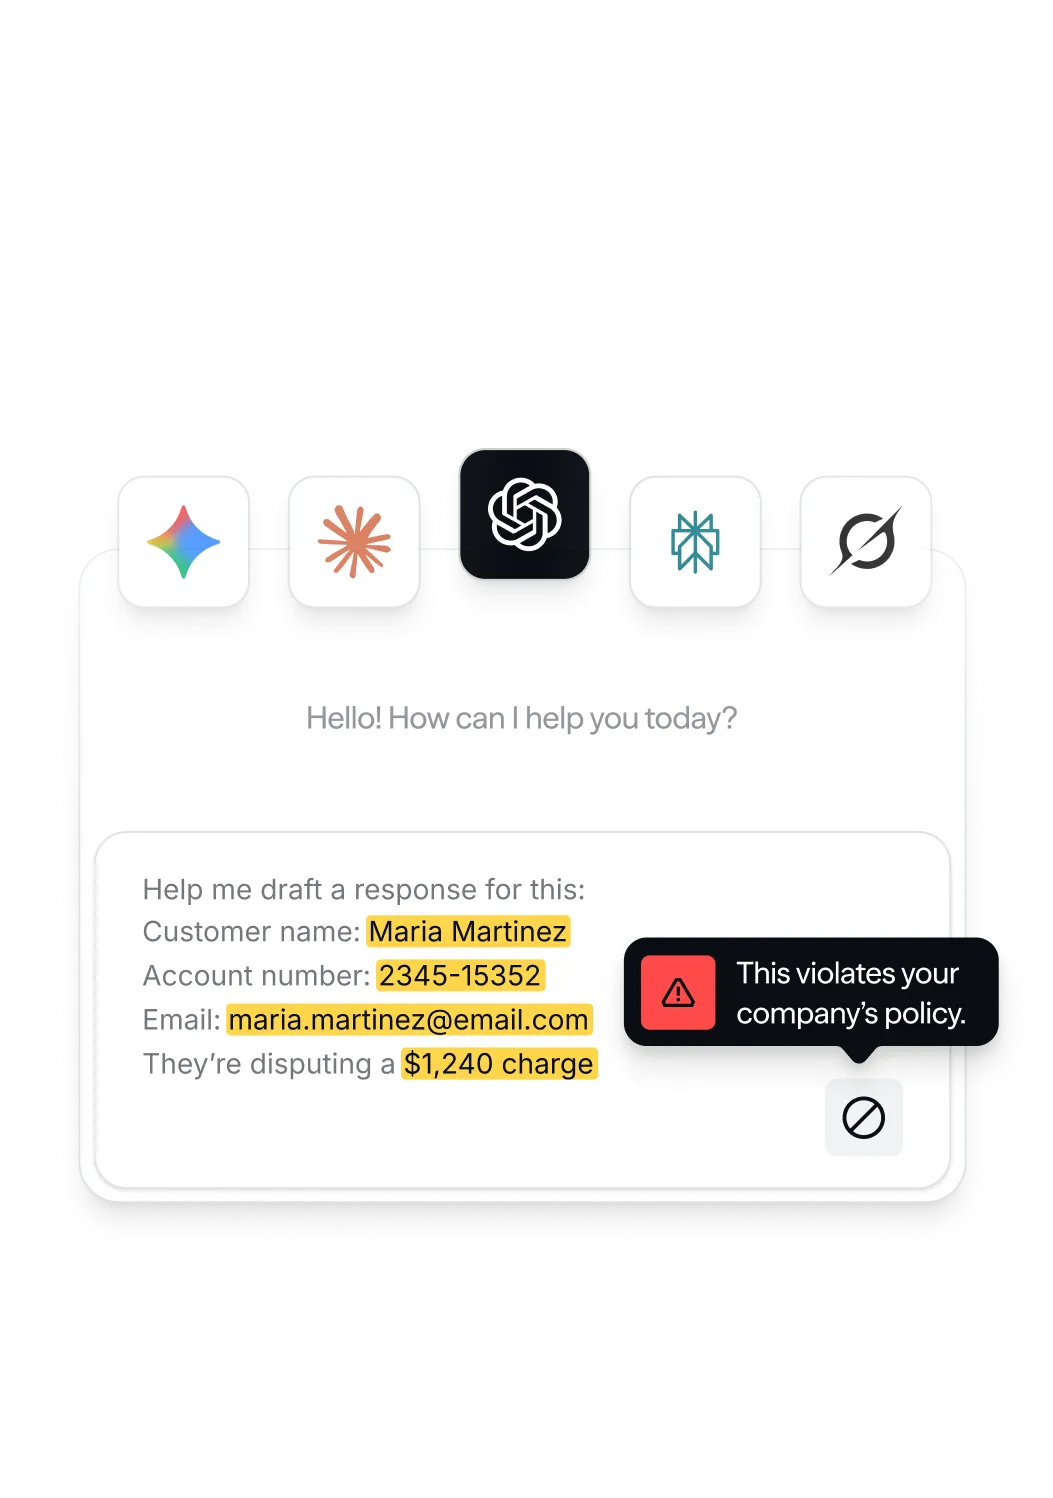
AI Governance
Secure risky AI usage and rogue agents
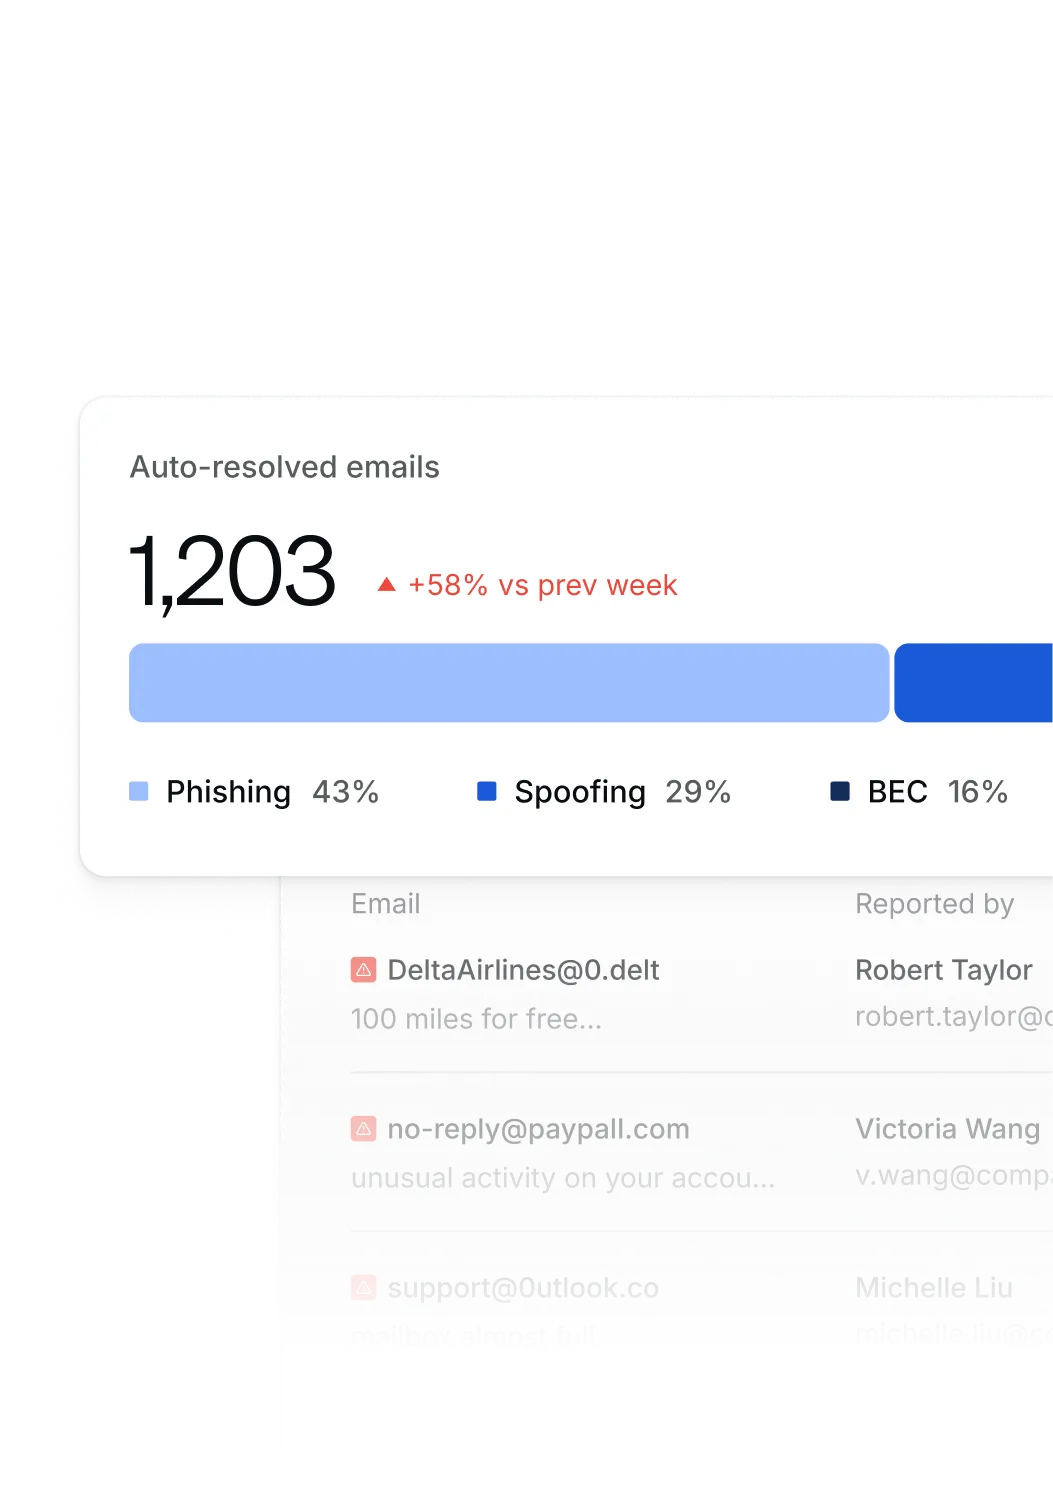
Phish Triage
Remediate user-reported phishing
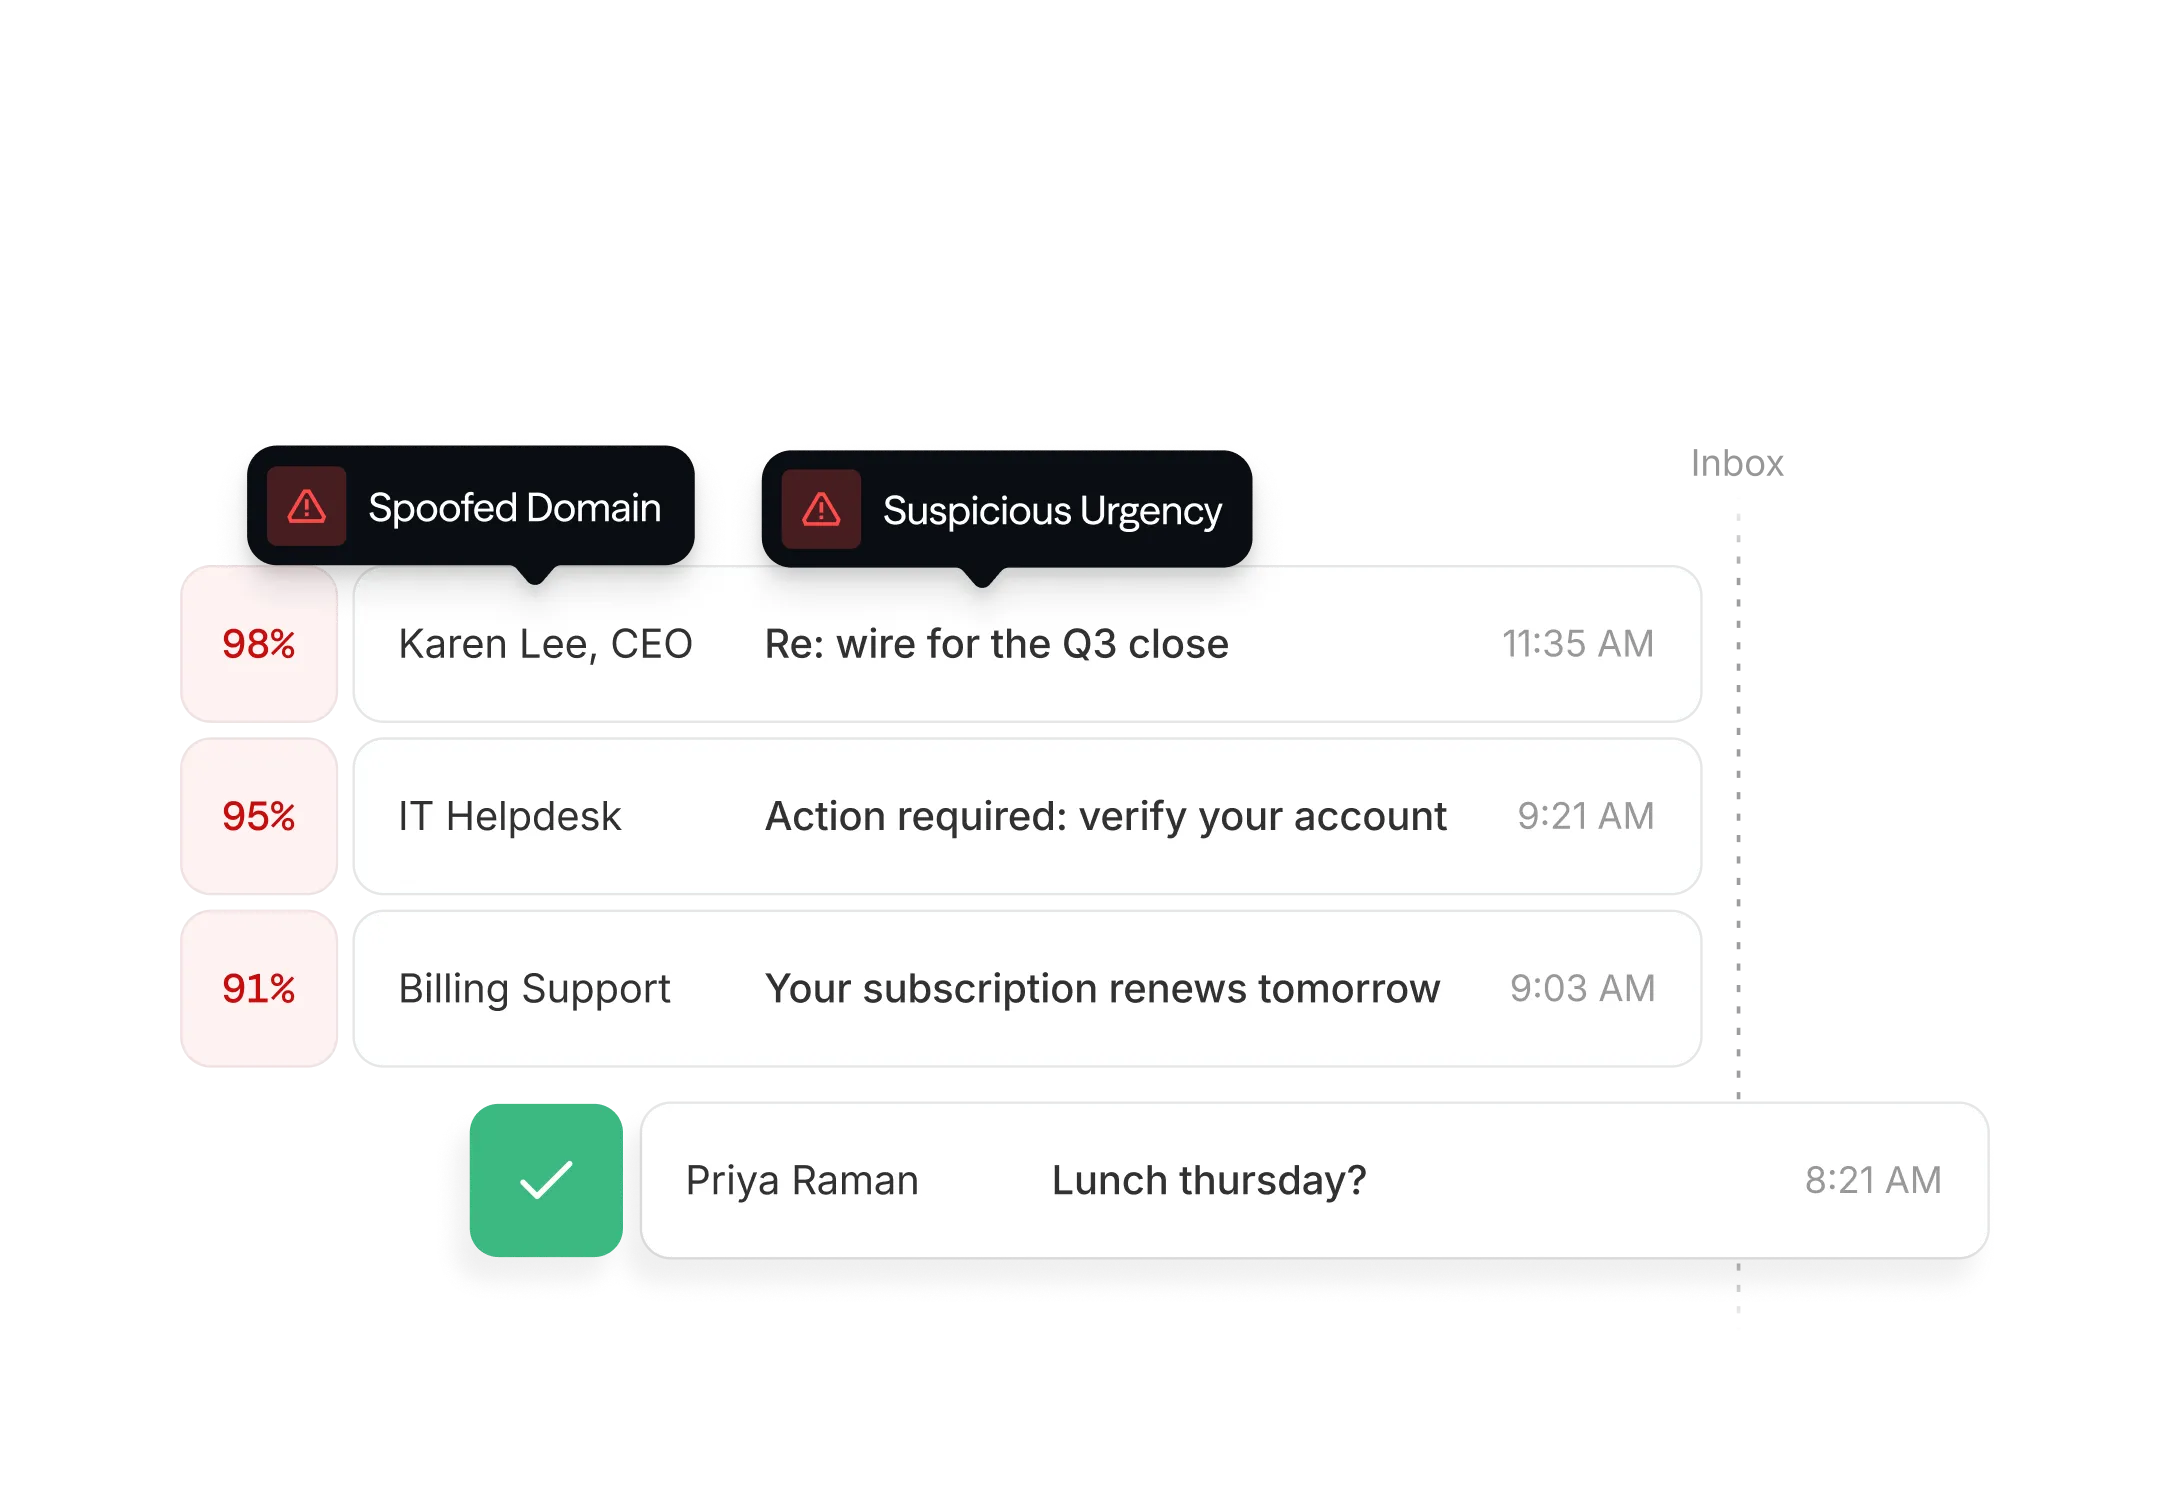
Email Security
Stop sophisticatedAI-powered email attacks
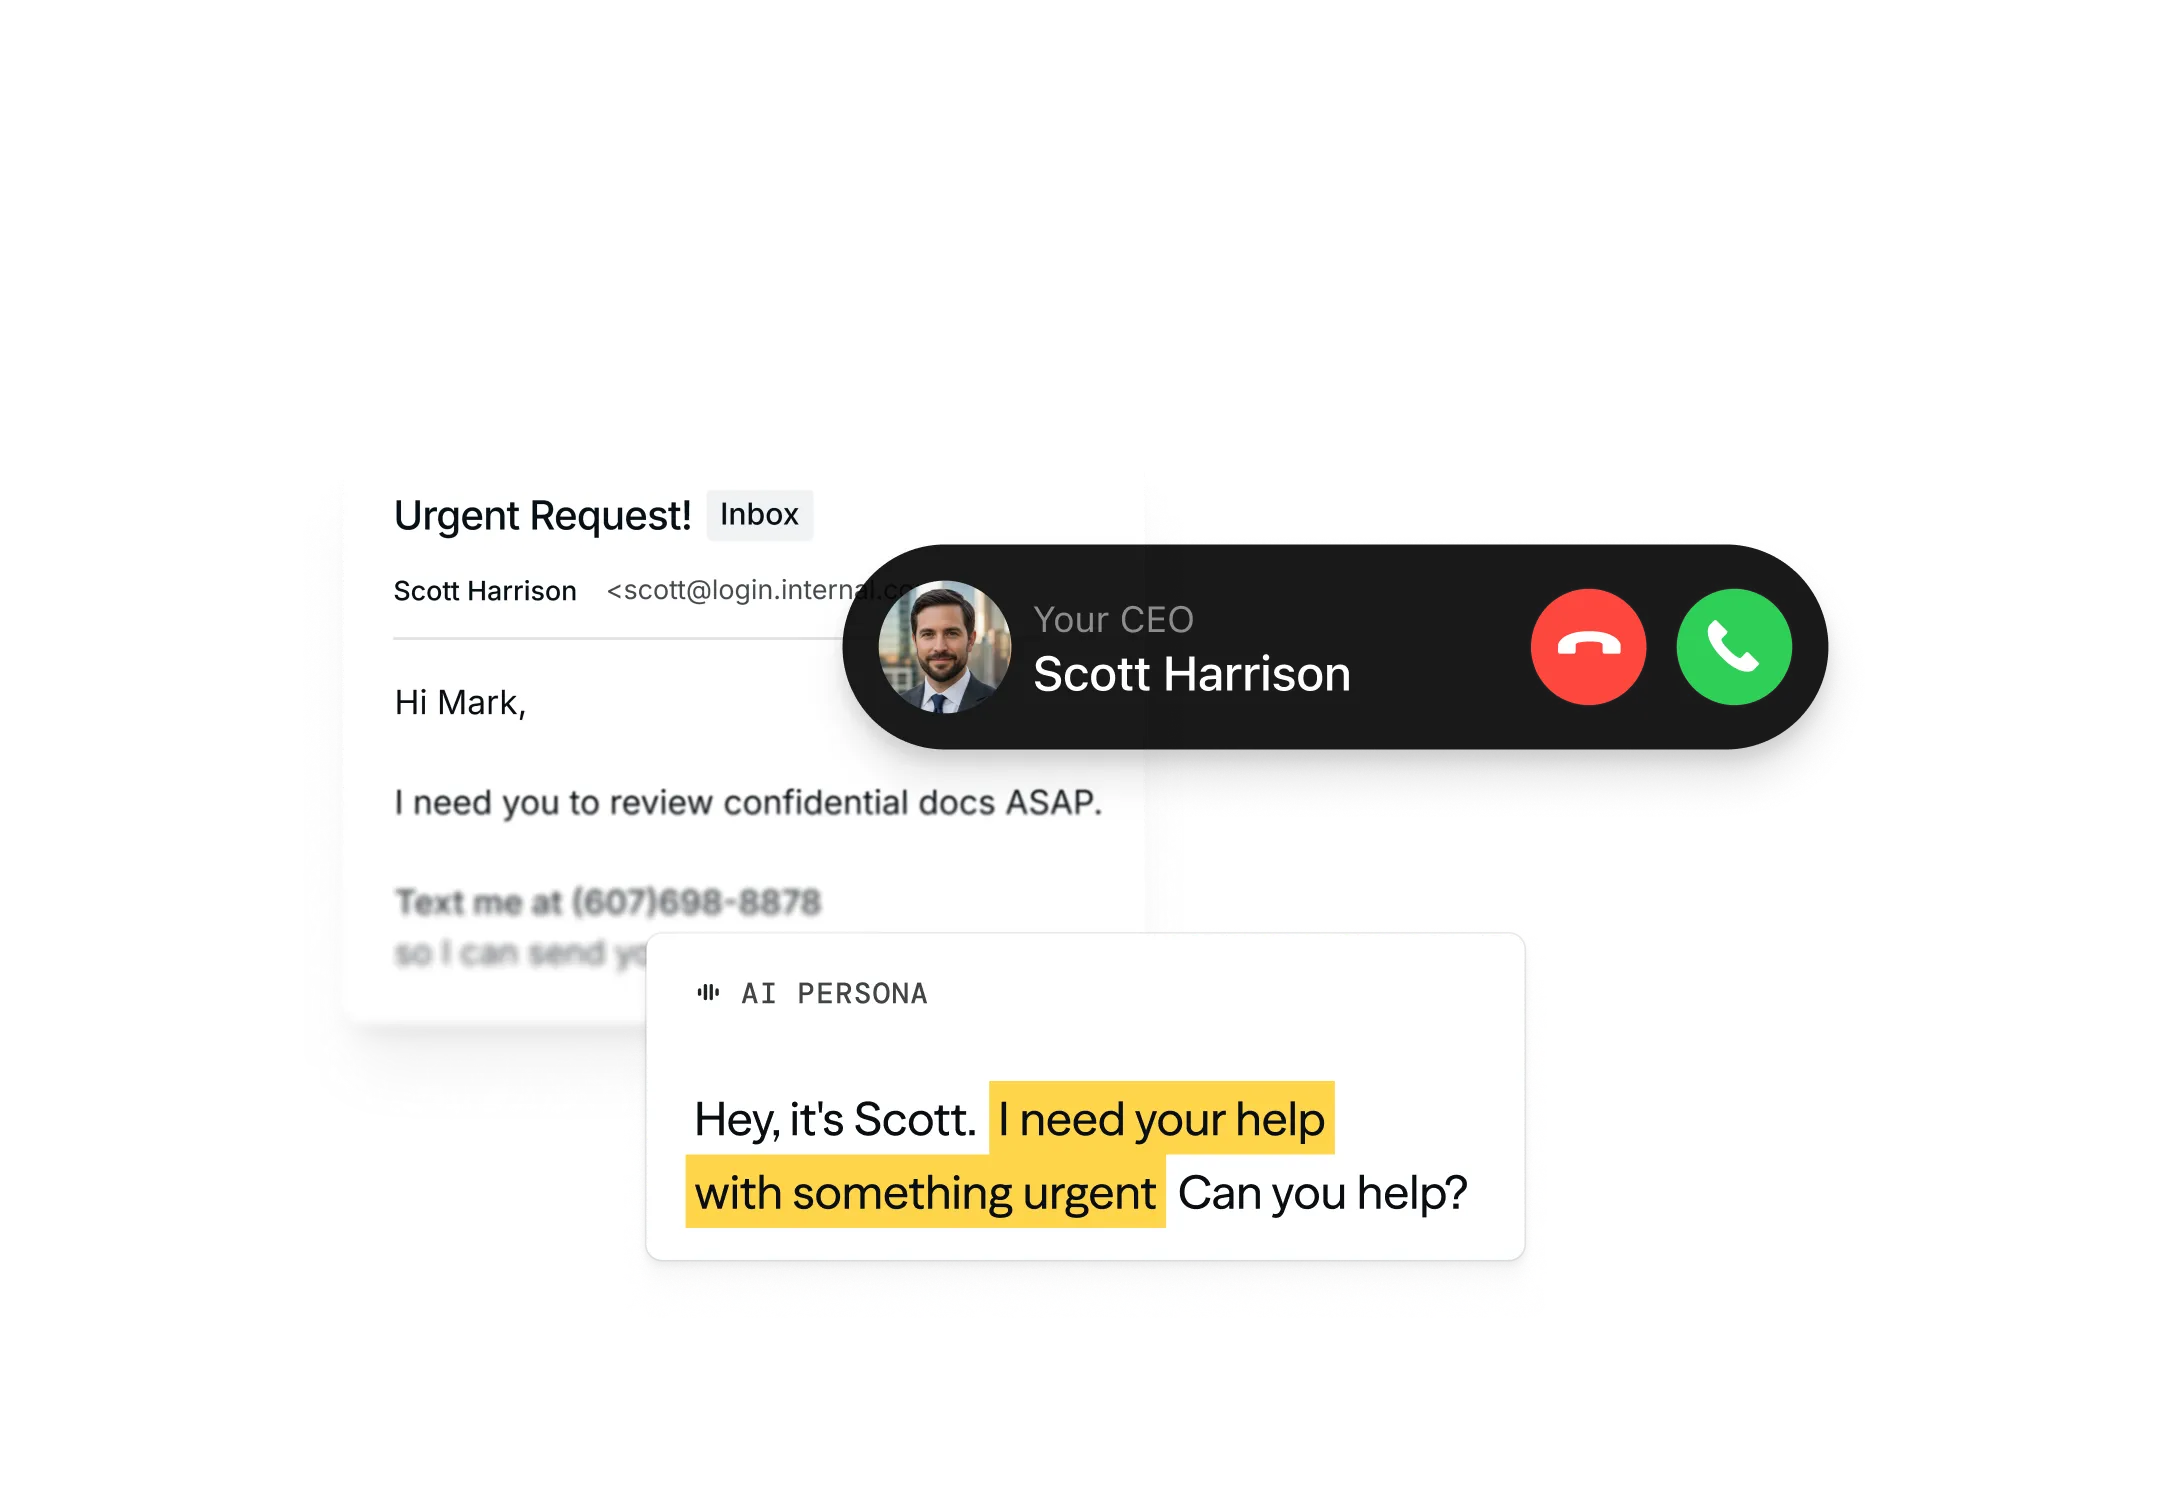
Phishing Simulations
Simulate multi-channel phishingattacks with AI
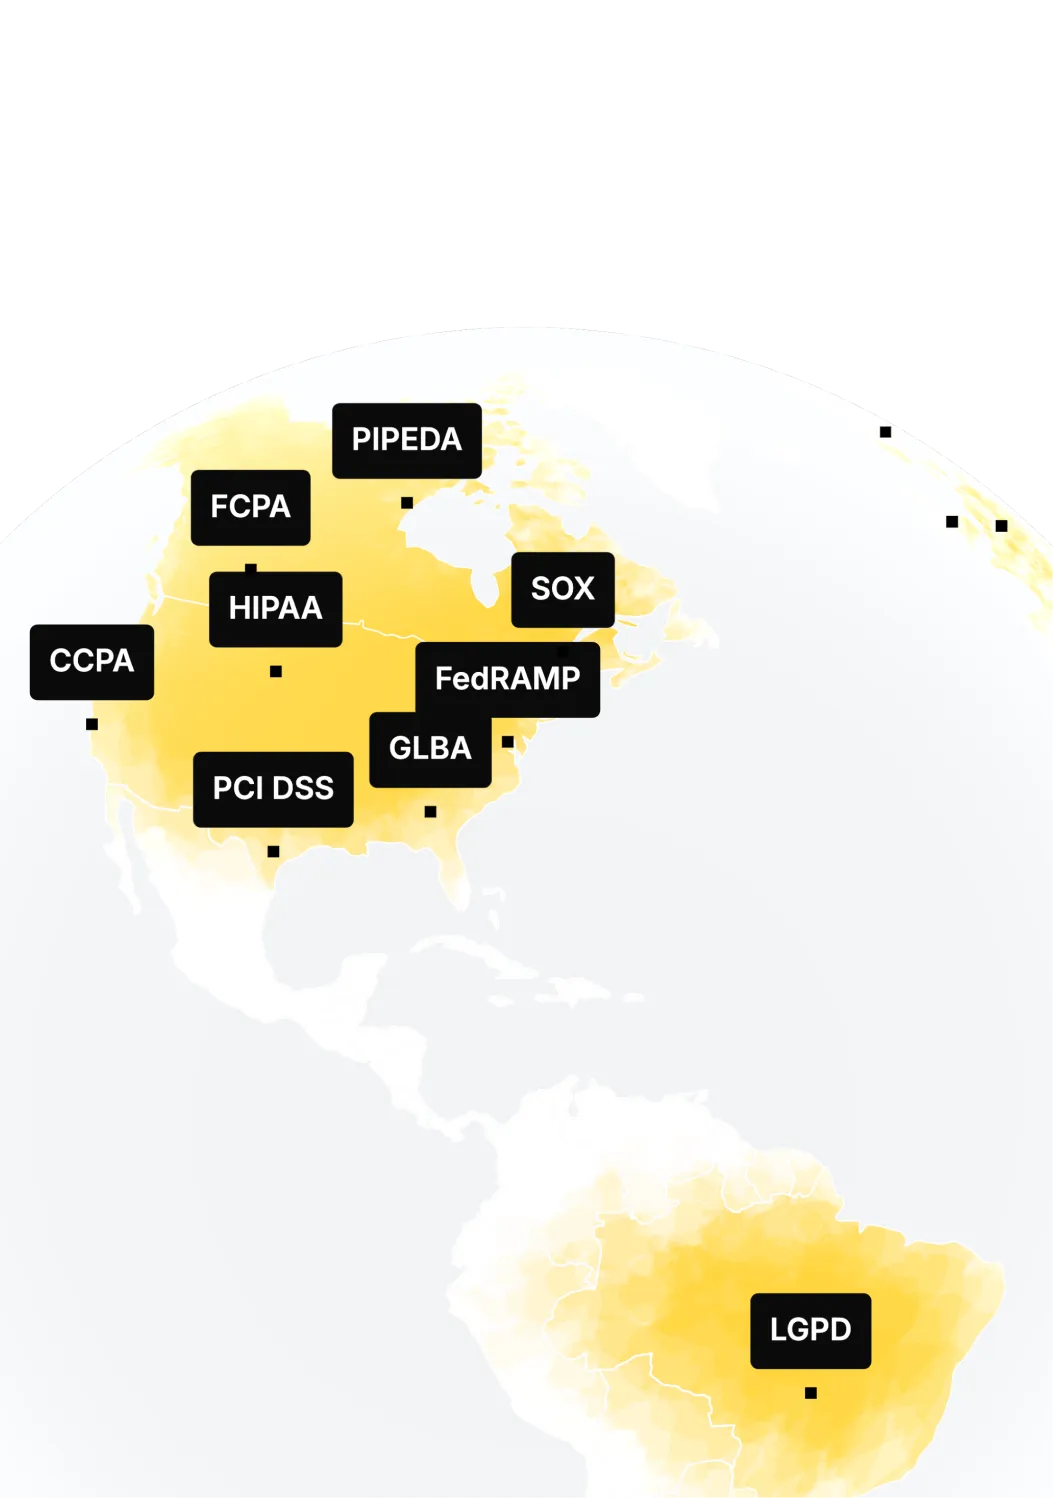
Compliance
Train for every regulatory framework
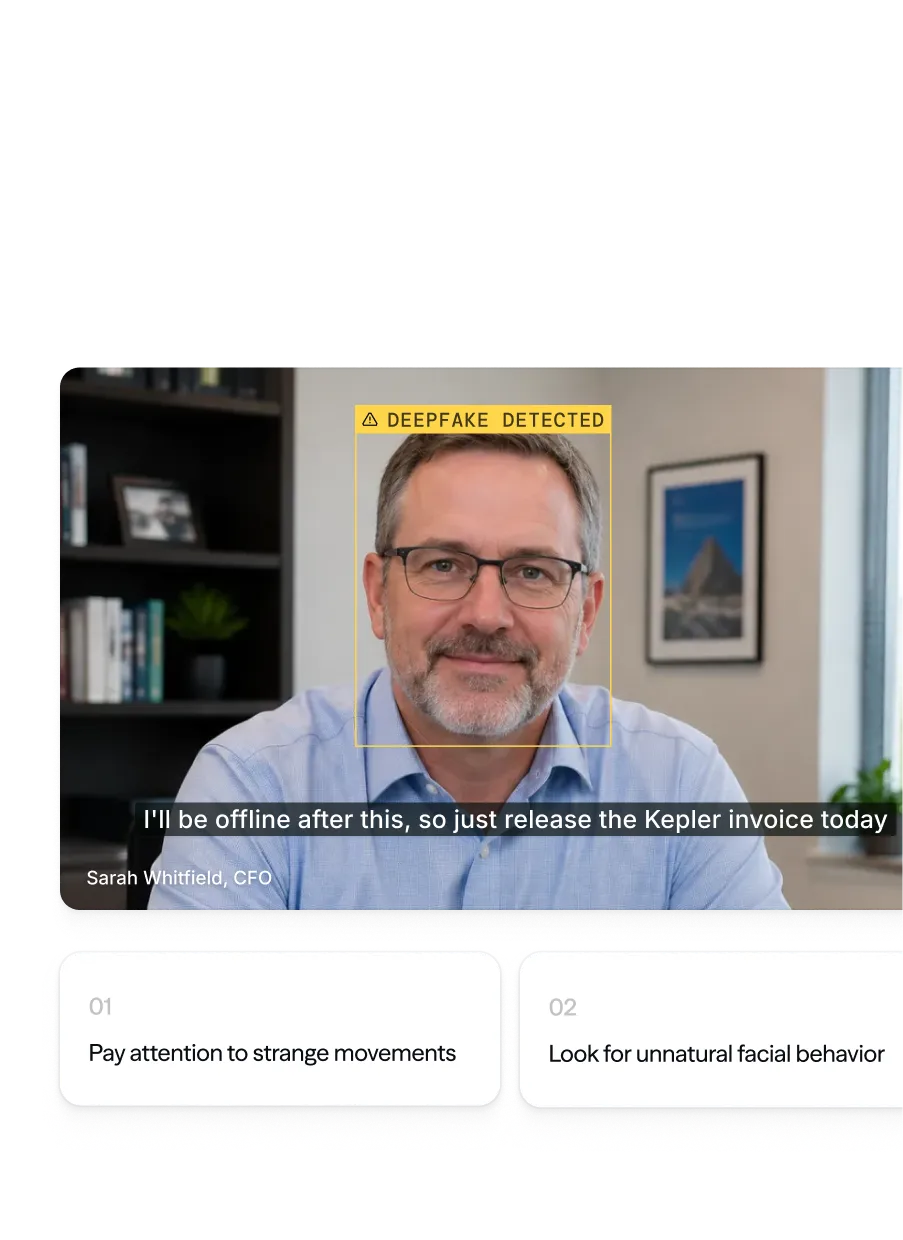
Security Awareness Training
Prepare your team against AI social engineering with interactive training
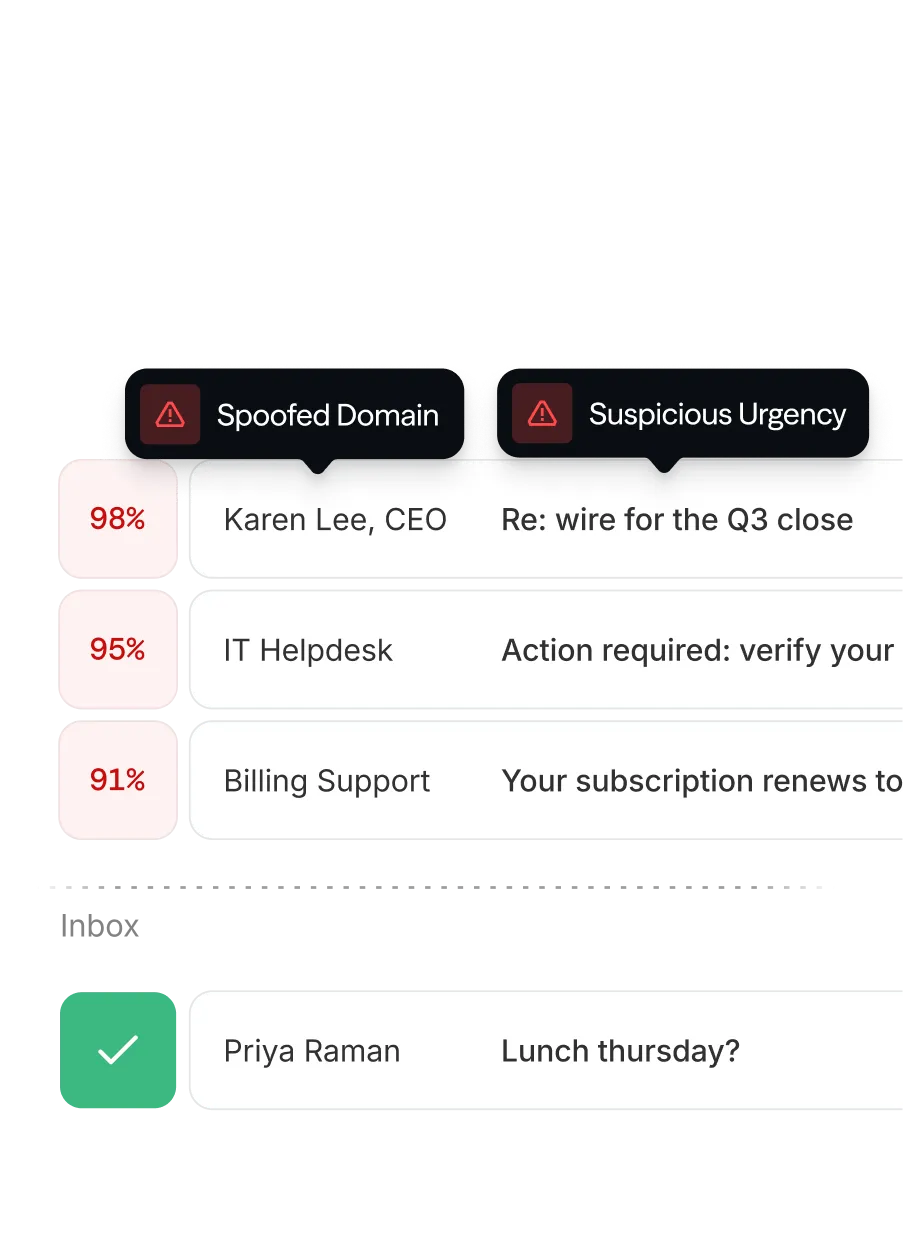
Email Security
Stop sophisticated AI-powered email attacks
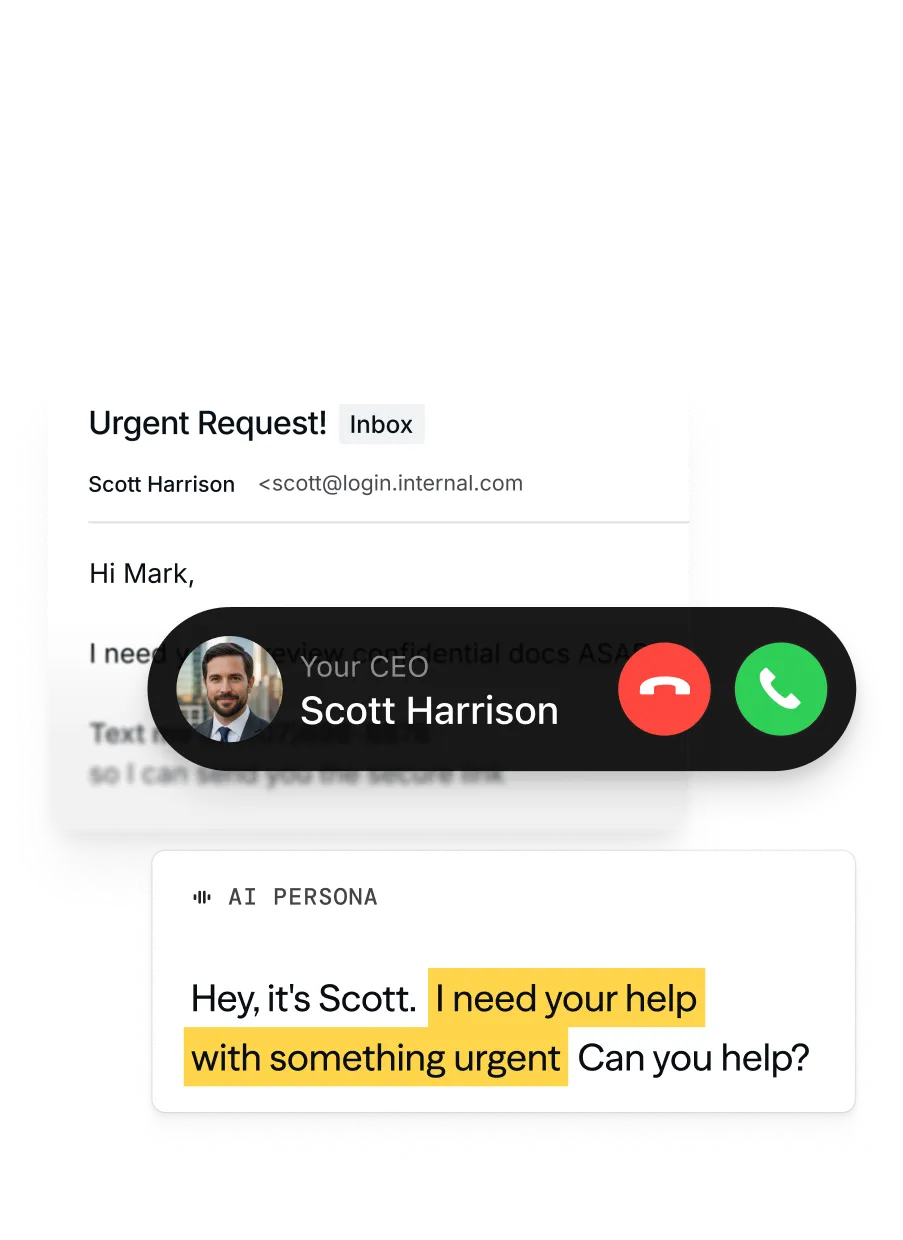
Phishing Simulations
Simulate multi-channel phishing attacks with AI
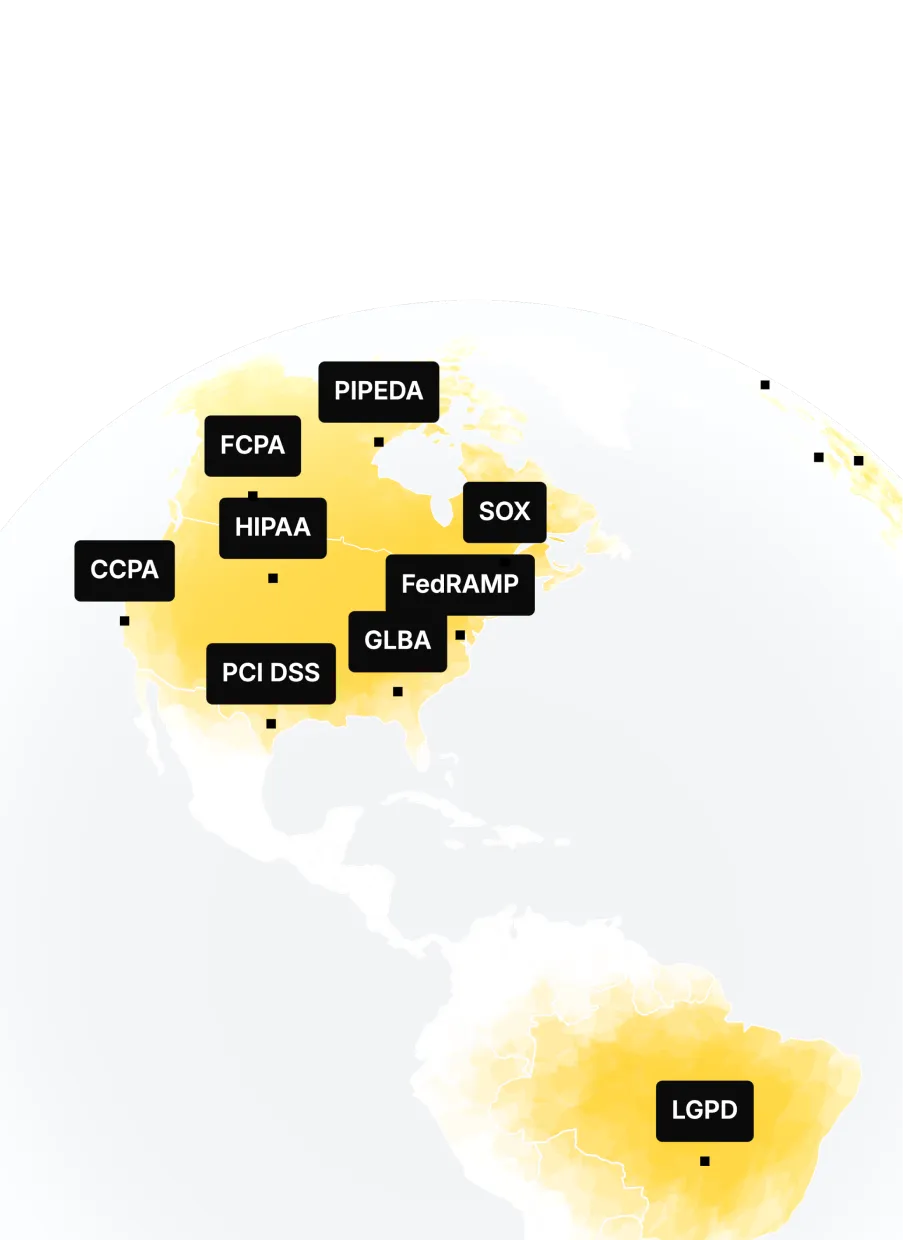
Compliance
Train for every regulatory framework
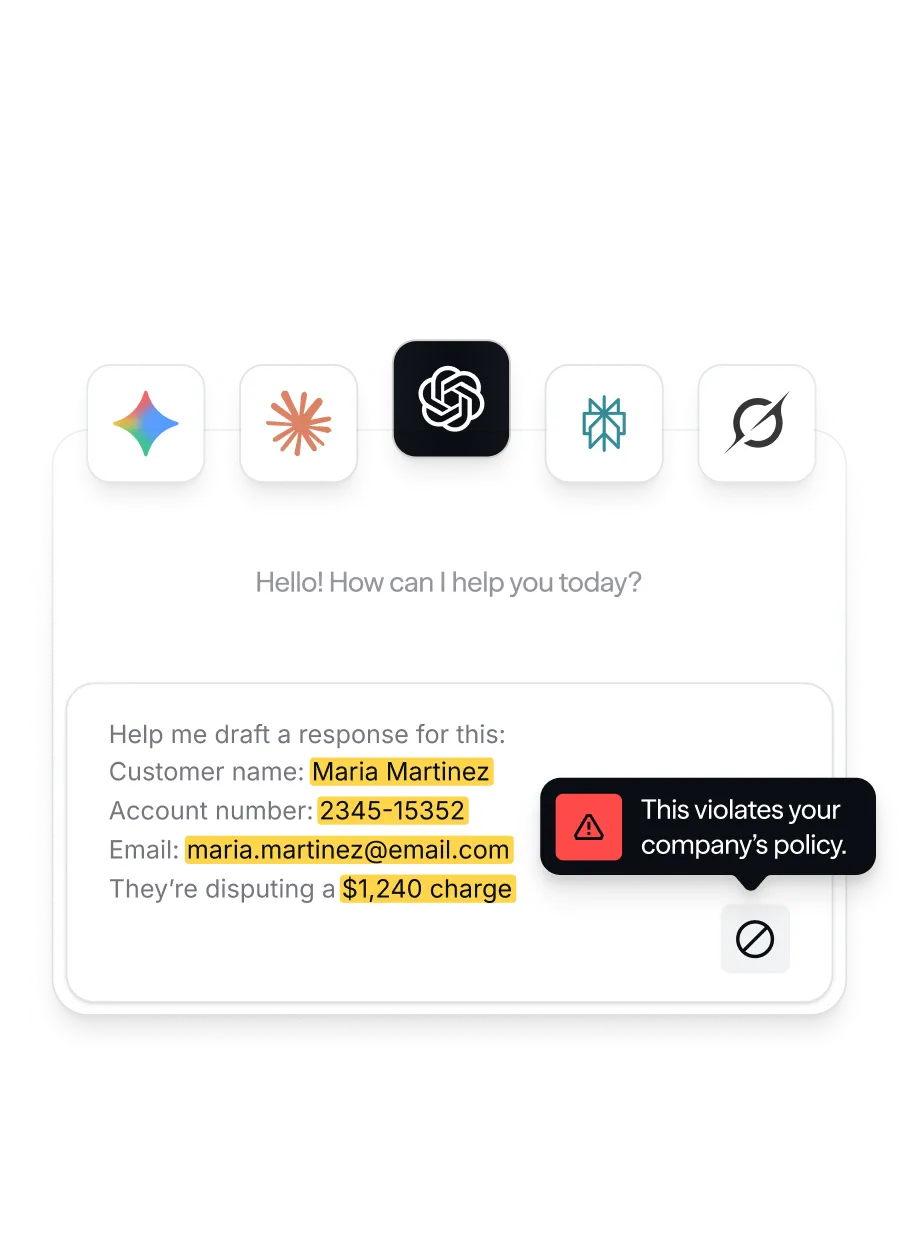
AI Governance
Secure risky AI usage and rogue agents
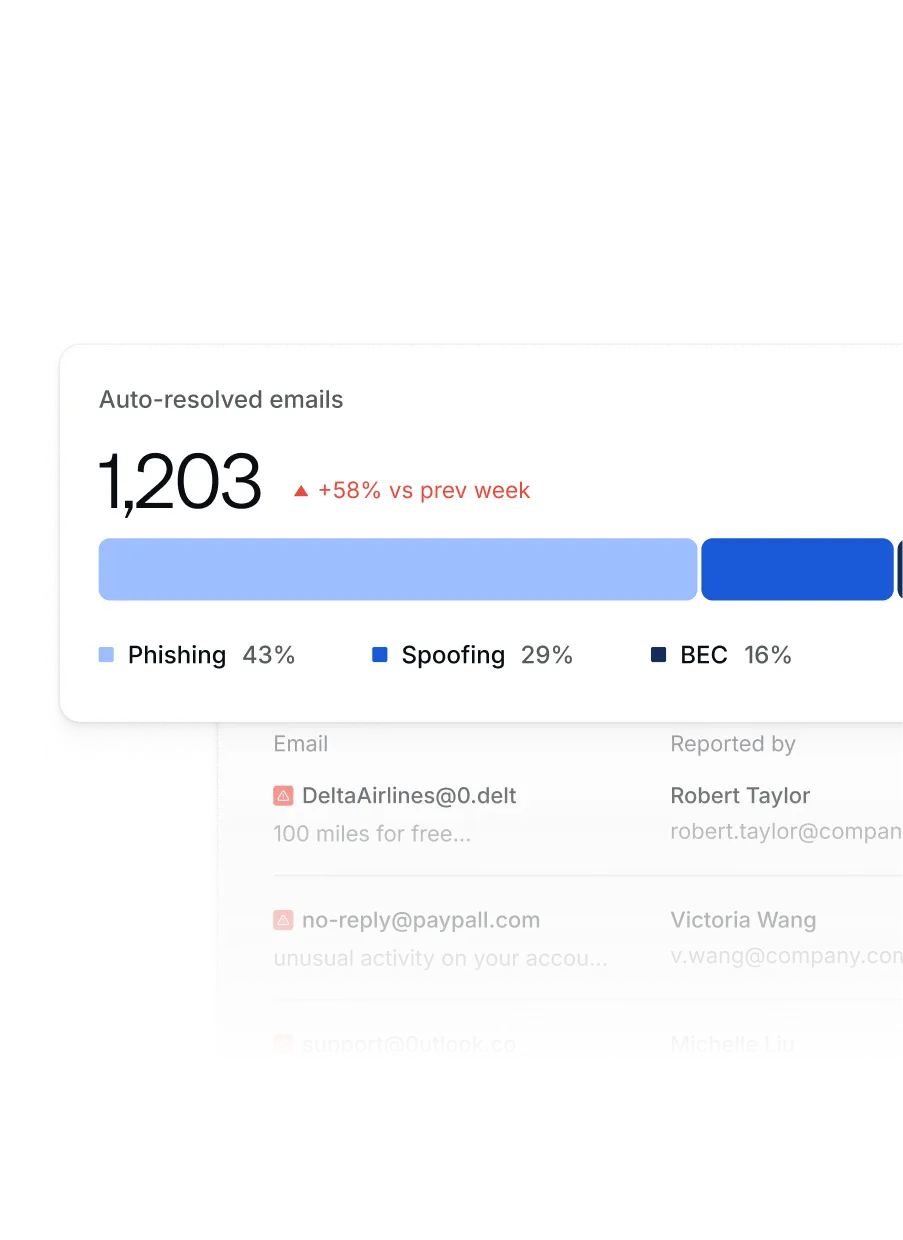
Phish Triage
Remediate user-reported phishing
Security Awareness Training
Prepare your team against AI social engineering with interactive training
Email Security
Stop sophisticated AI-powered email attacks
Phishing Simulations
Simulate multi-channel phishing attacks with AI
Compliance
Train for every regulatory framework
AI Governance
Secure risky AI usage and rogue agents
Phish Triage
Remediate user-reported phishing
Frequently Asked Questions.
Government employees are targeted by spear phishing attacks impersonating agency officials, deepfake voice and video attacks, SMS phishing, and nation-state social engineering campaigns designed to extract sensitive information or credentials. Adaptive trains employees on all of these scenarios using simulations built on real employee data and OSINT. Simulations replicate the specific impersonation tactics used against public sector organizations, so employees train on attacks that reflect what they are actually likely to face.
Yes. Many states now require annual cybersecurity awareness training for government employees by law, including Texas, New York, Florida, and Illinois, with requirements covering phishing awareness, ransomware, and social engineering. Adaptive provides the training infrastructure to meet these mandates with role-based assignments, automated completion tracking, and compliance reporting.
Yes. Adaptive is available through cooperative purchasing contract vehicles including NASPO ValuePoint and OMNIA Partners, which allow eligible government entities to purchase without running a competitive solicitation. Eligible agencies can reference these vehicles to move from decision to purchase in days or weeks rather than going through a full procurement cycle.
Yes. Training is role-based, so employees across IT, administration, legal, finance, and operational roles each receive content matched to their responsibilities and access levels. Agencies can also build custom training modules from internal policies using Adaptive's AI content creator, so content reflects agency-specific procedures rather than generic scenarios.
Adaptive simulates spear phishing emails built from real OSINT data, voice phishing calls using AI-generated personas that impersonate agency leadership or other officials, and SMS phishing scenarios. Simulations can replicate the exact type of impersonation attack a government employee is likely to see, so training reflects real-world threats rather than generic examples. When an employee fails a simulation, a short micro-lesson explains exactly what to look for next time.

